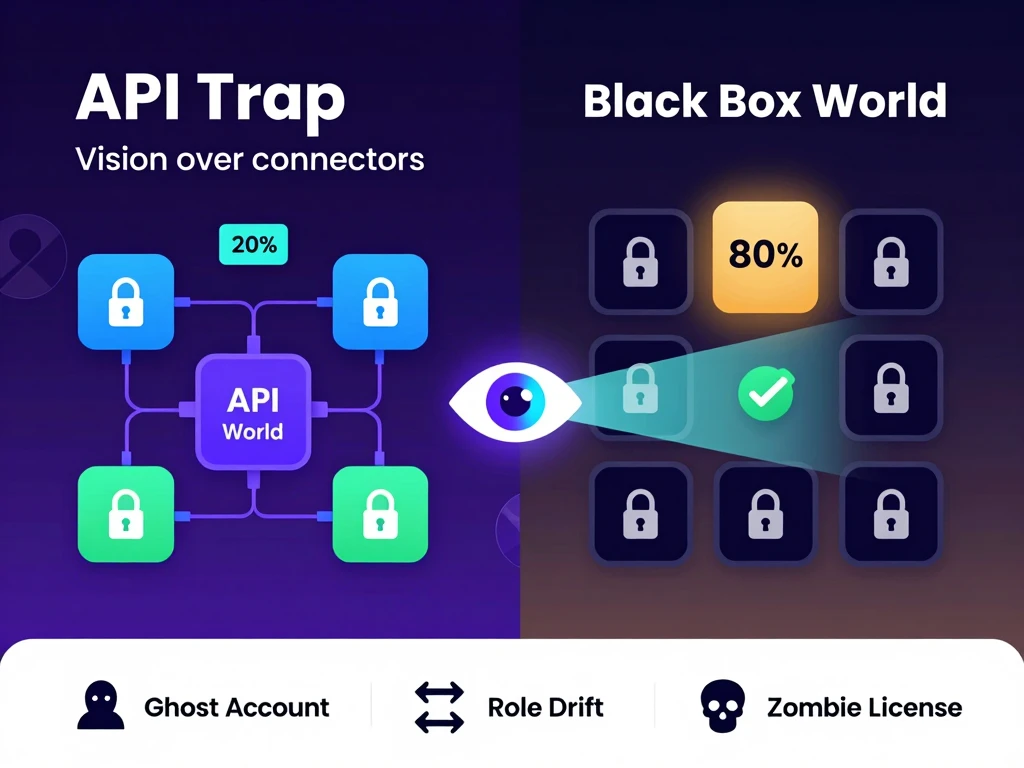
In the race to achieve ISO 27001 certification or a SOC 2 report, most fast-growing startups fall into the same trap: The API Integration Mirage.
Modern GRC platforms promise “automated compliance” by connecting to your tech stack via APIs. They hook into your GitHub, your AWS, and your Slack. It feels like magic—until you hit the “integration gap.”
The reality of 2026 is that the average mid-sized business now uses over 130 SaaS tools. For a CISO, only about 20% of those tools have robust, enterprise-grade APIs that traditional GRC tools can talk to. What happens to the other 80%? The niche project management tool your design team loves? The legacy HR portal? The internal database with no public endpoint?
They become “Black Boxes.” And in the world of compliance, a black box is a manual spreadsheet waiting to happen.
The Danger of “Security by Prayer”
When a tool can’t be integrated, security usually reverts to “manual verification.” An IT manager logs in, takes a look, and checkmarks a box. This is where the “Ghost Hunter” problem begins.
Research shows that 22% of security incidents involve insider threats—including former employees who retained access to systems because they were missed during a manual offboarding sweep. If you can’t automate the audit of a tool, you are effectively operating on “Security by Prayer”: praying that your manual checklist was 100% accurate.
Introducing AI Vision: The End of the Spreadsheet Era
At AutoCISO, we realized that the industry was fighting a losing battle. While everyone else is racing to build more API connectors, we decided to build “Eyes.”
AutoCISO is an AI-powered access intelligence platform that uses Computer Vision to audit applications from screenshots.
1. Screenshot-Based Capture
If an app has a “Users” list, you can capture it as a screenshot. You don’t need to wait for a developer to build an API integration or pay a “premium tier” tax just to get SCIM support. You simply upload a screenshot, and our AI Vision pipeline extracts the data.
2. The Screenshot Audit
Traditional manual audits take hours of cross-referencing spreadsheets. With AutoCISO, you upload a user list, and our Discrepancy Engine automatically flags:
- Ghost Accounts: Terminated employees who still have active logins.
- Role Drift: Users whose permissions don’t match their current department.
- Zombie Licenses: Accounts that haven’t been used in 90 days, draining your budget.
Moving Toward “Operational GRC”
Compliance shouldn’t be a bureaucratic exercise you perform once a year for an auditor. It should be an operational reality.
By moving away from the “API Trap” and embracing AI Vision, IT teams can finally gain visibility into the “Wild West” of their SaaS landscape. No more black boxes. No more manual spreadsheets. Just clear, vision-backed intelligence that keeps your organization secure.
Ready to hunt the ghosts in your machine?